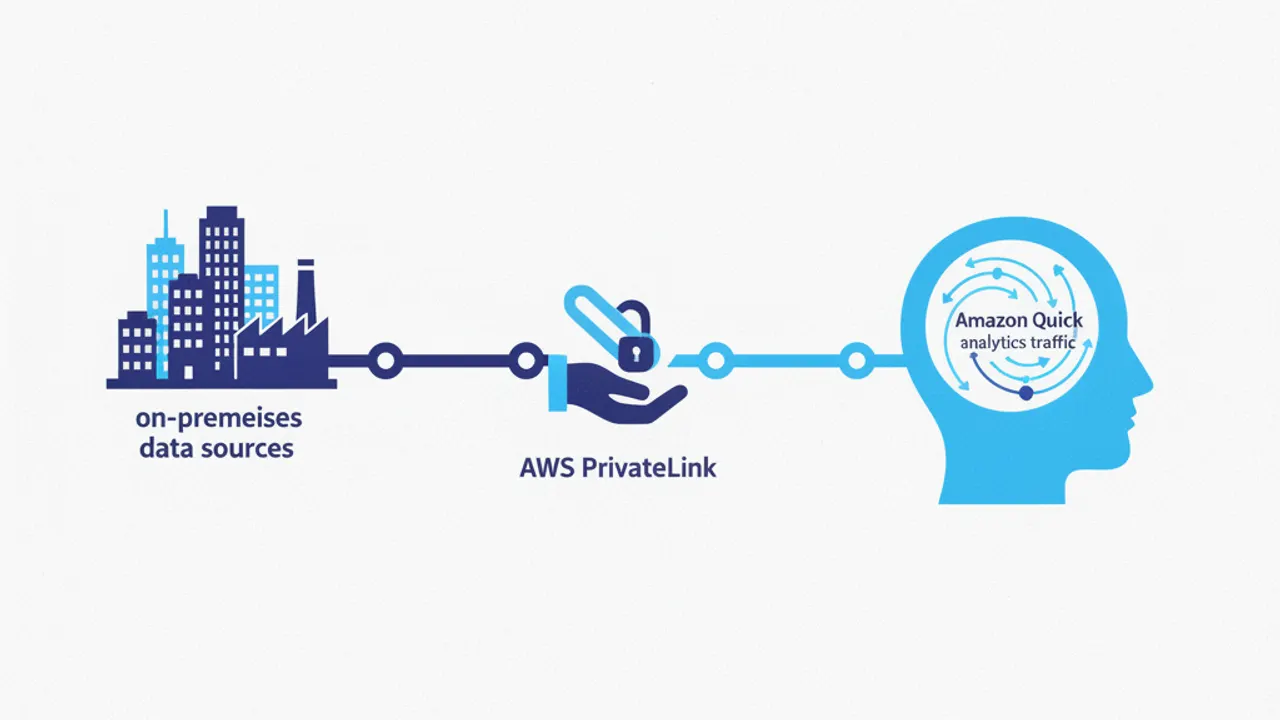
Amazon Web Services has detailed methods to connect on-premises data sources to Amazon Quick privately with AWS PrivateLink. This configuration focuses on keeping analytics traffic off the public internet during enterprise operations. The technical walkthrough systematically covers VPC endpoints for user and API access.
The guidance also examines the setup of VPC connections for data sources alongside DNS and endpoint policies. Additionally, the guide incorporates identity federation into the secure network architecture. Teams can leverage these mechanisms when enforcing VPC-endpoint-only access for compliance requirements.