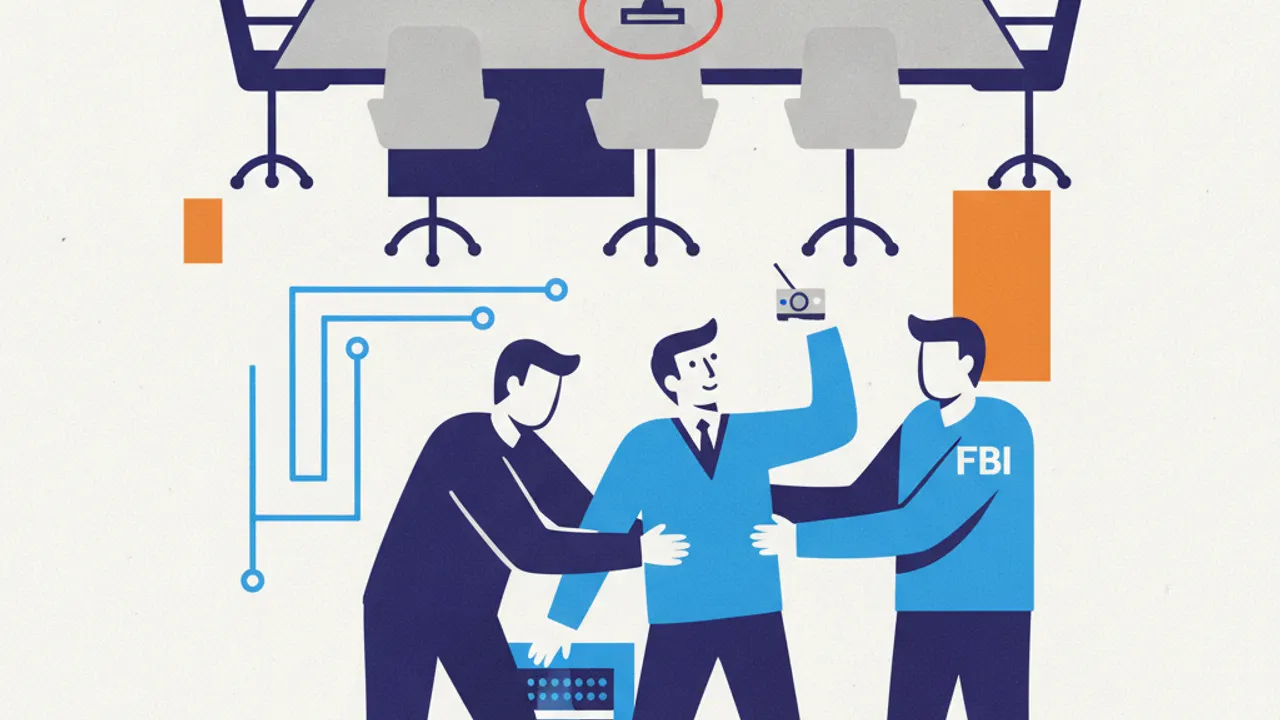
In San Francisco, investigators from the US Department of Justice and the Federal Bureau of Investigation have arrested software engineer Abdulrahman Alfozan. The 35-year-old OpenAI employee is accused of planting a bug or recording device inside an executive board conference room at the company's offices. The incident immediately prompted a federal criminal investigation.
According to filings associated with the US District Court for the Northern District of California, the device was placed to eavesdrop on confidential discussions and proprietary technological details. The targeted room is routinely used for strategic leadership meetings and discussions concerning protected frontier artificial intelligence developments. It remained undisclosed whether any intercepted audio had already been transmitted externally or remained stored on the hardware.
OpenAI discovered the recording device during internal checks and quickly contacted federal law enforcement. Rather than immediately confronting the suspect, the company coordinated its operational response with the FBI. System access privileges for Alfozan were gradually reduced by security teams to mitigate further data leakage while digital and physical evidence was preserved for legal proceedings.
Following the internal investigation, OpenAI handed the physical device and access logs over to the FBI, which led directly to the engineer's arrest. Alfozan now faces federal charges in Northern California concerning illegal interception of communications and unauthorized interference. Formal statements from his legal counsel were not immediately available following the custody order.
The case reignites intense industry concerns regarding physical security and insider threats within frontier artificial intelligence laboratories. Because proprietary research and foundation model blueprints carry immense economic and strategic value, corporate environments at leading labs are increasingly viewed as high-value targets. For technology leaders, the arrest serves as a reminder that traditional physical espionage techniques remain as critical a vulnerability as remote network intrusions.