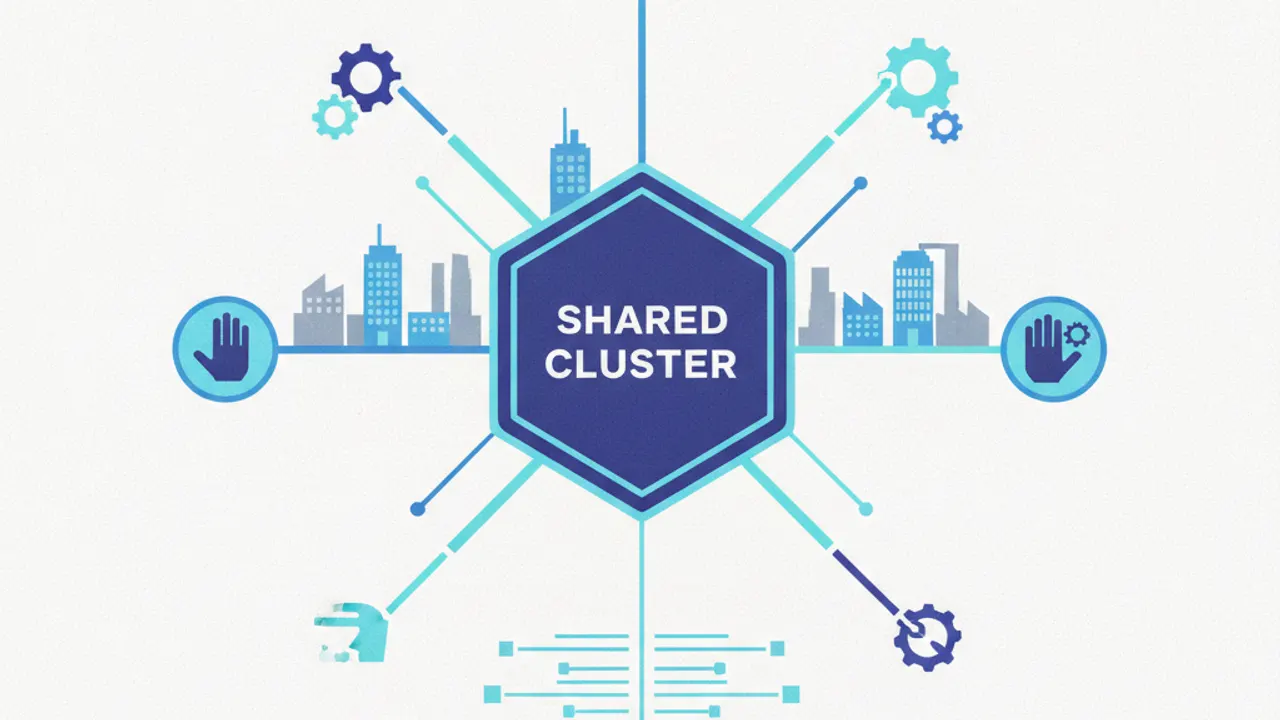
AWS has outlined a technical blueprint targeting organizations that manage shared high-performance computing environments. The documentation describes a "reference architecture for securely sharing one Amazon SageMaker HyperPod EKS cluster across multiple teams" without requiring separate clusters for each group. Within this setup, centralized access and user verification are handled by "using AWS IAM Identity Center for authentication."
To prevent cross-team interference, the architecture relies on "per-team SageMaker Domains and Kubernetes namespaces for isolation" across the computing environment. Resource distribution across competing workloads is regulated by deploying "HyperPod Task Governance for fairness" among the participating teams. Finally, financial visibility is supported by incorporating "namespace-level cost allocation for chargeback" to help administrators trace and assign cluster expenses.